







'We know how to find you': FBI issues direct video warning to ShinyHunters hacking group
Following the arrest of an alleged leader in the Netherlands, a top FBI cyber official released an unusual public address urging the remaining cybercriminals to turn themselves in "while the choice is still yours."
If you have ever filled out a job application, handed over your Social Security number for a background check or trusted an organization with information about your family, pay attention to what happened at the FBI.
The cybercriminal group ShinyHunters claims it compromised FBIJobs.gov and stole highly sensitive information connected to current and former FBI personnel and people who applied for jobs at the bureau. The group says its haul reaches far beyond basic contact information.
On Sept. 23, the FBI acknowledged the group's claims and said it was "actively and aggressively investigating" the incident. The bureau said investigators had not yet determined whether the point of breach involved an FBI system or a third-party provider supporting FBIJobs.gov.
That uncertainty is important. At the same time, samples provided to journalists contain enough real-world information to make the situation difficult to dismiss. For anyone whose details may be included, the potential fallout goes well beyond having an email address leaked.
FBI SAYS SOURCE OF ITS JOBS PORTAL BREACH STILL UNKNOWN AS HACKERS ALLEGE EMPLOYEE DATA COMPROMISED
Since that statement, the FBI has struck back by announcing the arrest of an alleged ShinyHunters leader in the Netherlands after a joint operation with Dutch authorities. Dutch police said a 24-year-old Amsterdam man was arrested Sept. 15.
Missed CyberGuy LIVE? Watch the replay and discover 5 ways AI can help you get better healthcare.
Our free CyberGuy LIVE class, Get Better Healthcare With AI, has ended, but you can still watch the full replay. Kurt "CyberGuy" Knutsson walks you through five practical ways AI can help you organize your health history, remember important appointment details, understand complicated medical information, research prescriptions and prepare smarter questions for your doctor. No technical experience is needed.
Watch the free replay + downloadable checklist now at CyberGuyLive.com
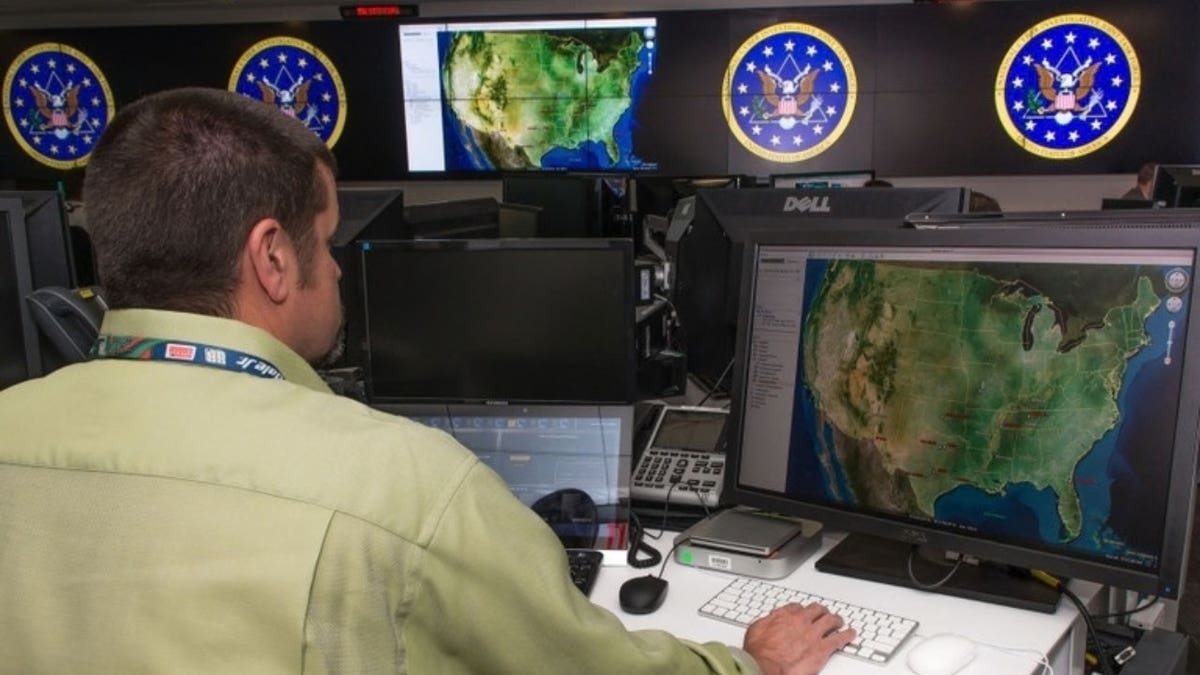
FBI investigators monitor digital threats as questions remain over how the FBIJobs.gov incident occurred and what information may have been exposed. (FBI)
What the FBI said about the FBIJobs.gov incident
In its Sept. 23 statement, the FBI addressed both the alleged compromise and the uncertainty surrounding where the attackers may have gained access.
"The FBI is aware of a cybercriminal enterprise group claiming a compromise of the fbijobs.gov portal," the bureau said. It added that the point of breach remained undetermined and said it was "actively and aggressively investigating this matter."
The FBI also said investigators were working closely with third-party providers that support FBIJobs.gov to reduce potential risk. The FBI confirmed the investigation and the unresolved question about where the breach occurred. It did not verify ShinyHunters' full account of what the group says it stole.
The FBI's Special Agent Applicant Portal also became unavailable as the incident unfolded. A notice posted Sept. 22 said FBIJobs.gov and the Special Agent Applicant Portal were unavailable. The applicant portal supports people who have progressed through portions of the special-agent hiring process, making the type of information potentially involved especially sensitive.
CyberGuy reached out to the FBI for an update on the incident, including whether employee or applicant data was accessed and whether affected individuals are being notified or offered identity protection. We did not hear back before our deadline.
The data sample raises much bigger concerns
ShinyHunters provided journalists with a spreadsheet containing about 5,000 alleged FBI personnel records. Reuters reported that the spreadsheet included names, home addresses, phone numbers, dates of birth, Social Security numbers and emergency contact information. It also included information about field office assignments and, in some cases, sensitive intelligence or counterespionage work.
Reuters said it could not authenticate the entire spreadsheet. However, reporters independently verified details belonging to more than 22 people by comparing the information with credit records and earlier leaked data. Reuters also matched career information or job titles for eight people against court filings, news reports, public profiles and online posts.
That still does not establish where every record came from. Real information can appear in several databases or previous breaches. Yet the matches add credibility to at least portions of the sample. 404 Media separately reported that the 5,000-person sample contained names, home addresses, phone numbers and information involving FBI employees' spouses.
Sensitive FBI assignments reportedly appeared in the data
The personal information alone creates obvious privacy concerns. The reported job information raises another level of risk. Reuters found records identifying people connected to China-related investigations, Russian intelligence work, human intelligence operations and electronic surveillance. Other entries referenced covert access, clandestine technical operations and telecommunications interception. Reuters said it could not verify that every assignment was authentic or up to date.
On Sept. 23, 404 Media also reported that the data appeared to expose members of the FBI's Remote Operations Unit. The outlet describes the ROU as a secretive FBI team involved in developing and using hacking tools to gain access to target devices. Think about what that combination of information could provide to someone with bad intentions.
A name may lead to a home address. An emergency contact could identify a spouse or child. Job information might reveal the kind of investigations someone works on. For an FBI employee working in a sensitive position, that creates risks far beyond ordinary financial fraud.
IS YOUR SOCIAL SECURITY NUMBER ON THE DARK WEB?
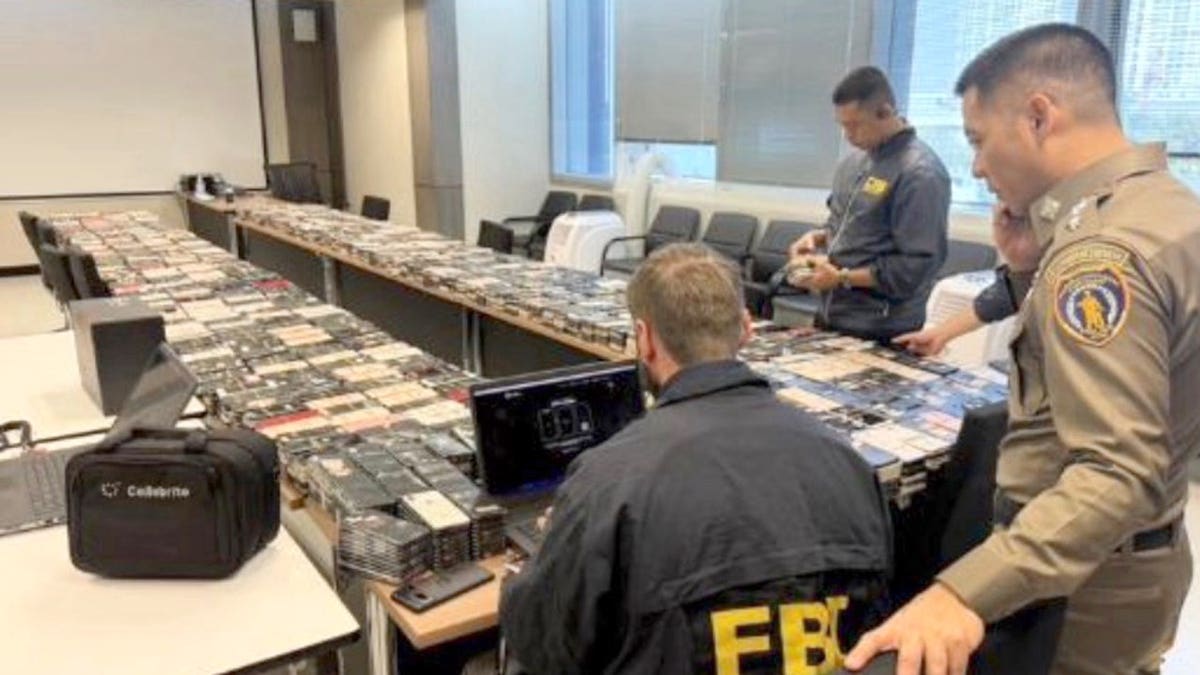
FBI cyber personnel work at computer stations as the bureau investigates claims that hackers accessed sensitive data tied to employees and job applicants. (FBI)
What ShinyHunters claims happened
ShinyHunters says it breached the FBI and stole between 2 and 3 terabytes of information connected to FBI personnel and job applicants. The group has also claimed that Justice Department worker data was obtained. The hackers claim they exploited a previously unknown vulnerability involving Oracle PeopleSoft, software used for human resources and other enterprise functions.
FBI documents reportedly show its recruiting operation uses PeopleSoft and AWS GovCloud. However, that does not prove the hackers' claimed method of attack. The alleged PeopleSoft vulnerability, the claimed 2-to-3-terabyte haul and a broader compromise of FBI systems had not been independently verified.
Reuters also reported that ShinyHunters claimed to possess files involving employee and applicant vetting, contracted background investigations and sensitive medical information. Reuters said it could not verify what additional information the hackers actually possessed. That caveat is critical. ShinyHunters has an obvious interest in making its access sound as extensive as possible. For now, there are signs that portions of the information supplied by the hackers correspond to real people. Major questions about the source, scope and attack path remain unresolved in the FBI's public statement.
Why ShinyHunters says it targeted the FBI
ShinyHunters says retaliation, rather than a demand for money, motivated the attack. The group points to warnings the FBI issued about ShinyHunters-related cyber activity earlier in 2026. On May 15, the FBI's Internet Crime Complaint Center published an advisory describing ShinyHunters as a cybercriminal group specializing in large-scale data breaches and extortion.
The advisory warned that actors using the name may use real or exaggerated claims about stolen information to pressure victims. It also described threatening communications, harassment of family members and swatting among tactics associated with ShinyHunters actors. ShinyHunters disputes portions of the FBI's description of its activities. Reuters reported that the group said it targeted the FBI because of the May warning and said it was holding the allegedly stolen data while demanding that the bureau rescind the statement.
Why you should care even if you never worked for the FBI
You may read a headline about FBI employees and assume this has little to do with you. Yet the way the alleged data could be abused should feel familiar to anyone who has handed personal information to an employer, bank, health provider, insurance company or government agency. Organizations often collect far more than your name and email address. They may hold your home address, Social Security number, birthdate, employment history and emergency contacts. Job applications can contain years of background information.
You may have done everything right and still have that information exposed because the organization holding it or one of its technology providers was attacked. That third-party piece deserves attention here. In its Sept. 23 statement, the FBI specifically said investigators had not determined whether the breach point involved its own enterprise or a third party.
The same setup exists throughout everyday life. Your employer might use an outside payroll provider. Your doctor's office may rely on billing software from another company. Retailers routinely send information through outside payment systems. Once you hand over your personal data, you often have little visibility into how many systems eventually store or process it.
FBI headquarters in Washington, D.C. The bureau is investigating ShinyHunters’ claims that sensitive personnel and applicant data was stolen. (Kevin Carter/Getty Images)
Stolen personal details make scams much harder to spot
Suppose someone emails you and knows your full name, employer and home address. Then the person mentions your spouse or a job application you actually submitted. That message feels very different from a generic scam email. This is why personal data can be so useful to attackers. They can combine stolen records with information already available from data brokers, social media or previous breaches. The result can be a phishing message tailored closely enough to make you hesitate before questioning it.
Cybercriminals could pose as an FBI recruiter or someone from an employer's human resources department. They could even claim they are contacting you to help protect information exposed in the breach. The FBI's May advisory warned that stolen personal information can help attackers create targeted campaigns and pressure victims.
What FBI applicants, employees and families should do now
Even while investigators work to establish the full scope, anyone who believes their information may be involved can take precautions.
1) Verify every unexpected FBI-related message
If you applied for an FBI job, be suspicious of calls, texts or emails claiming you need to reenter information because of the portal incident. Do not use a link or phone number contained in an unexpected message. Contact your existing applicant coordinator or reach the FBI through a channel you already know. The FBI's own ShinyHunters guidance recommends verifying unusual requests through another method before responding.
2) Warn family members and emergency contacts
This step becomes particularly important because the reported sample included spouses and emergency contacts. Tell people listed on employment or application records to be cautious if someone suddenly knows their connection to you. Criminals may target a relative because they expect that person to have fewer security safeguards. If someone claims there is an urgent problem involving you, an employer or law enforcement, verify the story independently before sharing information or sending money.
3) Freeze your credit if your Social Security number may be exposed
A credit freeze can make it harder for someone to open a new credit account in your name. You need to place the freeze separately with Equifax, Experian and TransUnion. The FTC says credit freezes are free and remain in place until you lift them. A freeze will not prevent every form of identity theft. Continue monitoring accounts you already have.
4) Consider getting an IRS Identity Protection PIN
If your Social Security number may have been exposed, an IRS Identity Protection PIN can help protect you from tax identity theft. The six-digit IP PIN prevents someone else from filing a federal tax return using your Social Security number or Individual Taxpayer Identification Number. Anyone with an SSN or ITIN who can verify their identity can request one. Keep the number private. The IRS says it will never call, email or text you asking for your IP PIN.
5) Watch financial, tax and medical activity
Look for new accounts you do not recognize, unfamiliar charges or changes to existing accounts. Also pay attention to unexpected IRS notices, rejected tax filings and medical bills or insurance explanations of benefits for treatment you never received. These can signal types of identity theft that a credit freeze alone may not stop. If you discover identity theft, report it through IdentityTheft.gov and follow the recovery plan for the information that was compromised.
6) Strengthen your online accounts before phishing begins
Neither Reuters nor the FBI's Sept. 23 statement said passwords were included in the 5,000-record sample. Still, exposed personal details can make attempts to steal your passwords much more convincing. Use a unique password for every important account. A password manager can help keep track of them. Turn on two-factor authentication (2FA) or passkeys wherever available. Also be cautious about unexpected password-reset requests.
7) Keep strong antivirus protection running on your devices
A personalized phishing message can still contain a malicious link or infected attachment. Strong antivirus software can help detect known phishing websites, malicious downloads and malware before they compromise your device. That gives you another layer of protection if a convincing email or text gets through. Security software cannot replace careful clicking, but it can help when a scam looks unusually believable. Get my picks for the best 2026 antivirus protection winners for your Windows, Mac, Android and iOS devices at CyberGuy.com.
8) Reduce how much personal information strangers can find
If your home address, phone number and relatives already appear on people search sites, leaked records can give criminals even more information to work with. Search for yourself online and review what is publicly visible. You can request removal from many data broker and people search sites yourself or use a personal data removal service to handle recurring opt-out requests. Reducing what is publicly available gives a criminal fewer pieces to combine with information from a breach. Check out my top picks for data removal services and get a free scan to find out if your personal information is already out on the web by visiting CyberGuy.com.
9) Use dark web monitoring as an early warning
Dark web monitoring can alert you when information tied to your email address, phone number, Social Security number or other identifiers appears in known breach collections. Some identity theft companies include Dark Web Monitoring that searches for exposed personal information and alerts you when it is found. However, treat an alert as a warning rather than proof that someone has stolen your identity. Monitoring cannot prevent information from circulating once criminals obtain it. Its value comes from giving you an opportunity to secure affected accounts, watch for fraud and take action sooner. See my tips and best picks on best identity theft protection at CyberGuy.com.
10) Do not pay someone who claims to have your data
The FBI's guidance involving ShinyHunters recommends against paying or engaging with threat actors making demands. Save threatening communications instead. Preserve screenshots, email addresses, phone numbers and other identifying information. You can report cybercrime through the FBI's Internet Crime Complaint Center at IC3.gov. If someone appears to face an immediate physical threat, contact emergency services.
Kurt's key takeaways
There are still major unanswered questions about the FBIJobs.gov incident. The FBI's Sept. 23 statement left the point of breach unresolved, and the bureau had not publicly validated ShinyHunters' claim that it stole between 2 and 3 terabytes of data. Still, the data samples deserve serious attention. Reuters verified details belonging to more than 22 people and reported that the spreadsheet contained Social Security numbers, home addresses, dates of birth, emergency contacts and information about sensitive assignments. What concerns me most is how useful those pieces become when they are connected.
A criminal who knows where you work, where you live and who your spouse is has a much easier time building a scam that feels authentic. For FBI personnel tied to intelligence or covert technical work, the exposure could create security concerns that reach well beyond financial fraud. The takeaway for the rest of us is practical. You cannot control the security of every employer, government agency or company holding your information. You can control how much information about you remains publicly available, how strongly your accounts are protected and how quickly you respond when something suspicious appears.
If information this sensitive can potentially be exposed through a system connected to the FBI, how confident are you about the employers, companies and government agencies holding your personal data? Let us know by writing to us at CyberGuy.com.
Sign up for my FREE CyberGuy Report
- Get my best tech tips, urgent security alerts and exclusive deals delivered straight to your inbox.
- For simple, real-world ways to spot scams early and stay protected, visit CyberGuy.com – trusted by millions who watch CyberGuy on TV daily.
- Plus, you'll get instant access to my Ultimate Scam Survival Guide free when you join.
CLICK HERE TO DOWNLOAD THE FOX NEWS APP
Copyright 2026 CyberGuy.com. All rights reserved.
